
Keeps a second Bitwarden or Vaultwarden vault in sync with your main one, with encrypted backups of both.
Getting started | Documentation | Releases | Discussions


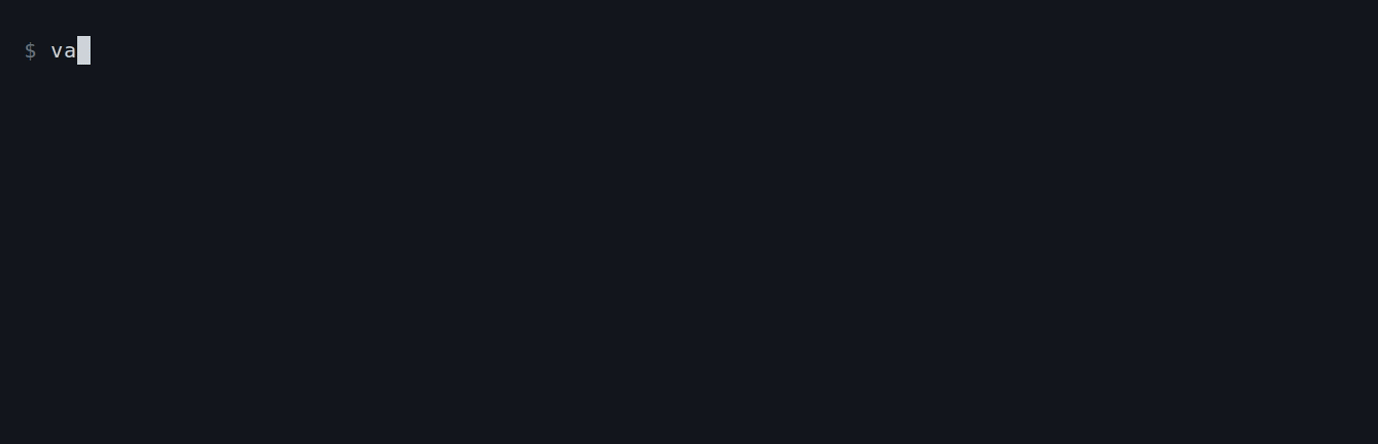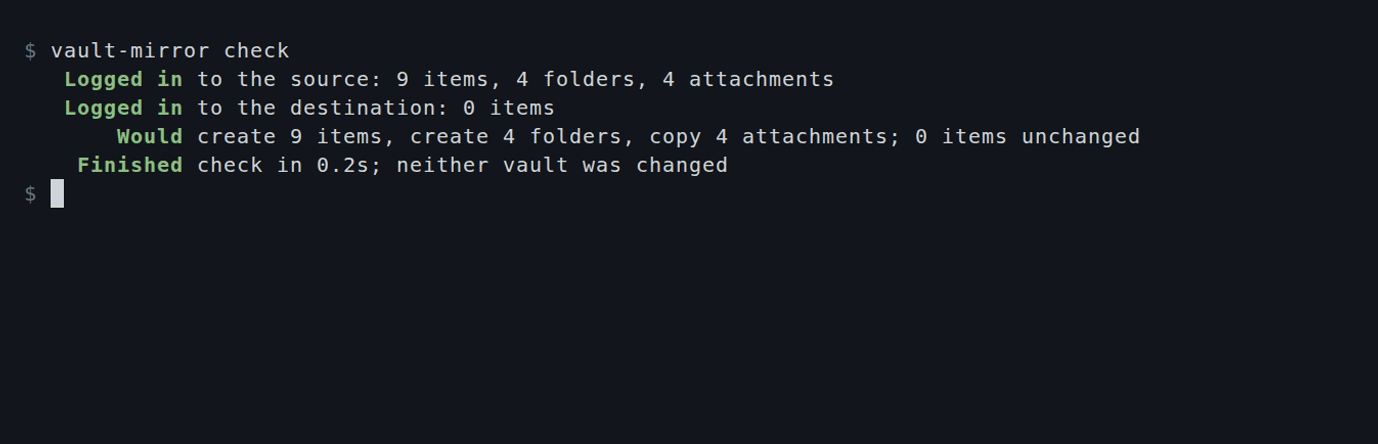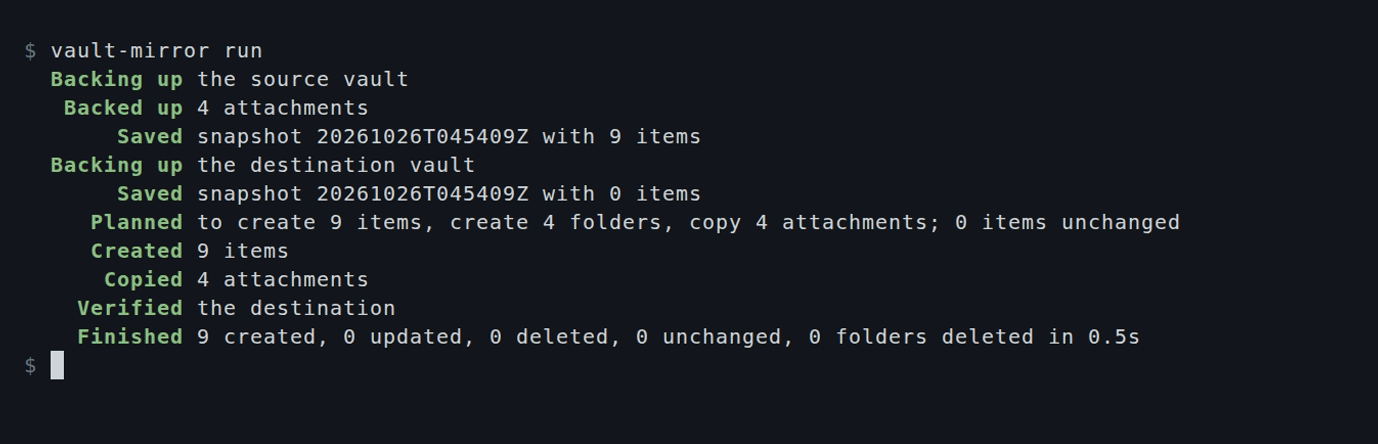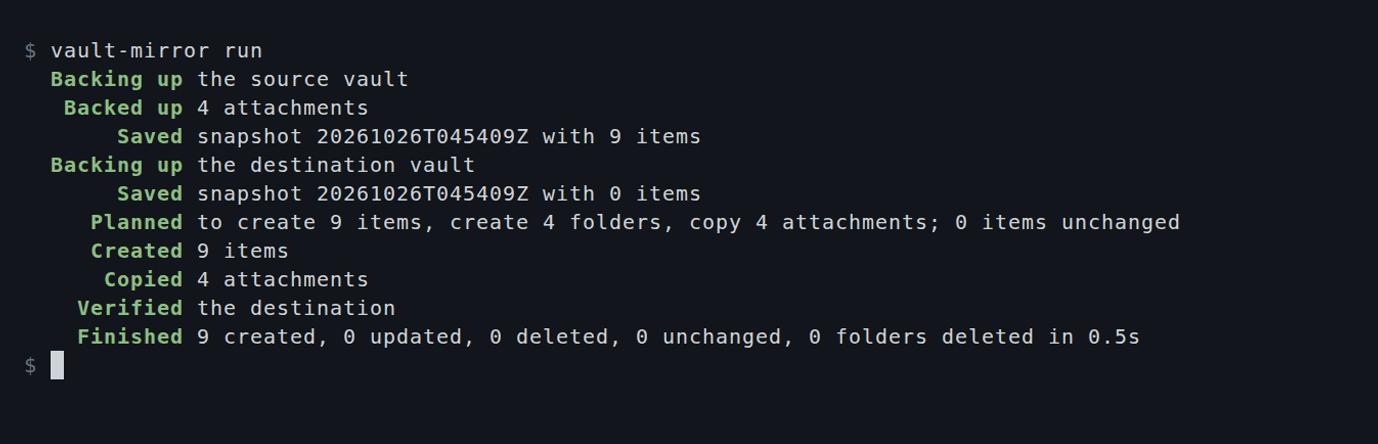
vault-mirror copies your main vault, the source, into a second vault, the destination, and keeps it up to date. Each run:
- backs up both vaults, encrypted with age,
- creates, updates and deletes items until the destination matches the source,
- reads the destination back to check the result.
Changes go one way. Items you add to the destination stay, and runs stop rather than overwrite changes to copies found at the start of a run. Changes during a run can still be lost.
For ongoing organization mirroring, prefer a Vaultwarden destination. Updates to existing Bitwarden organization copies stop by default. You can explicitly allow updates that can erase members' private metadata.
Use it to keep a working copy on Bitwarden's cloud for when your own server is down, to move between servers, or to share one folder or collection with another account.
- Copies every item type, custom field, passkey, password history, folder, collection and attachment, within server limits.
- Saves backups as encrypted Bitwarden exports, which you can decrypt with
ageand import into any Bitwarden app. - Stops before runs that look like a mistake, such as swapped vaults or an empty source. See safety checks.
- Runs as one binary or a container, without the
bwCLI or Node.js.
You need Docker, your main account, and a second account for the destination. vault-mirror stores both accounts' API keys and master passwords; see Security for what that means.
Both servers must show every supported item type, even if your vault holds only logins. Bitwarden servers, including the cloud, can hide newer types and block runs. Check the server restrictions before setup.
-
In the web vault of each account, open Settings → Security → Keys and select View API key. Keep both pages open.
-
Create a directory and run the setup. It asks for both accounts and writes
vault-mirror.envandcompose.yaml.mkdir vault-mirror && cd vault-mirror docker run --rm -it --user "$(id -u):$(id -g)" -v "$PWD:/work" -w /work \ ghcr.io/nikitamgrimm/vault-mirror:0.9 init
-
Start it:
docker compose up -d
vault-mirror now runs on the schedule you chose. Getting started explains each step.
The container image runs on linux/amd64 and linux/arm64:
docker pull ghcr.io/nikitamgrimm/vault-mirror:0.9The releases page has binaries for Linux (x86-64, arm64), macOS (Apple silicon, Intel) and Windows (x86-64, arm64), with checksums and build provenance.
With Rust installed, use cargo-binstall or cargo:
cargo binstall vault-mirror          # the release binary
cargo install vault-mirror --locked  # or build from source
The macOS binaries aren't notarized. If you downloaded one in a browser, allow it to run with:
xattr -d com.apple.quarantine vault-mirror- Getting started: a first setup, step by step.
- How it works: what a run does, copies, and the safety checks.
- Configuration: every setting, organizations, and mirroring part of a vault.
- Backups and restoring: the backup directory, and getting data back out.
- Commands and scheduling: every command, scheduling, and systemd.
- Limitations: what isn't copied, and server restrictions.
- Questions: short answers to common questions.
- Security: what vault-mirror can access and what it stores.
Ask questions in Discussions and report bugs in Issues. vault-mirror's logs contain no secrets or vault content, so you can paste them. Report security problems privately, as SECURITY.md describes.
See CONTRIBUTING.md.
vault-mirror is licensed under the GPL-3.0-only, like Bitwarden's
bitwarden-crypto crate that it uses.
This is an independent project. It isn't affiliated with or endorsed by Bitwarden, Inc. or the Vaultwarden project.