Repository navigation
argocd pods lose IAM access for the first few minutes #7494
Unanswered
balusarakesh
asked this question in
Q&A

Replies: 1 comment 1 reply

|
I'm not sure whether this could qualify as a bug in Argo CD. We do not provide the repo server deployment with a ServiceAccount mount by default. When you use the default installation manifests for e.g. upgrade from one version to another, chances are that your manifests in the cluster (with a ServiceAccount mounted to repo-server pod) is overwritten with the vanilla version (which do not mount a ServiceAccount to the pod). |
1 reply

|
|
Sign up for free
to join this conversation on GitHub.
Already have an account?
Sign in to comment


Uh oh!
There was an error while loading. Please reload this page.
Description
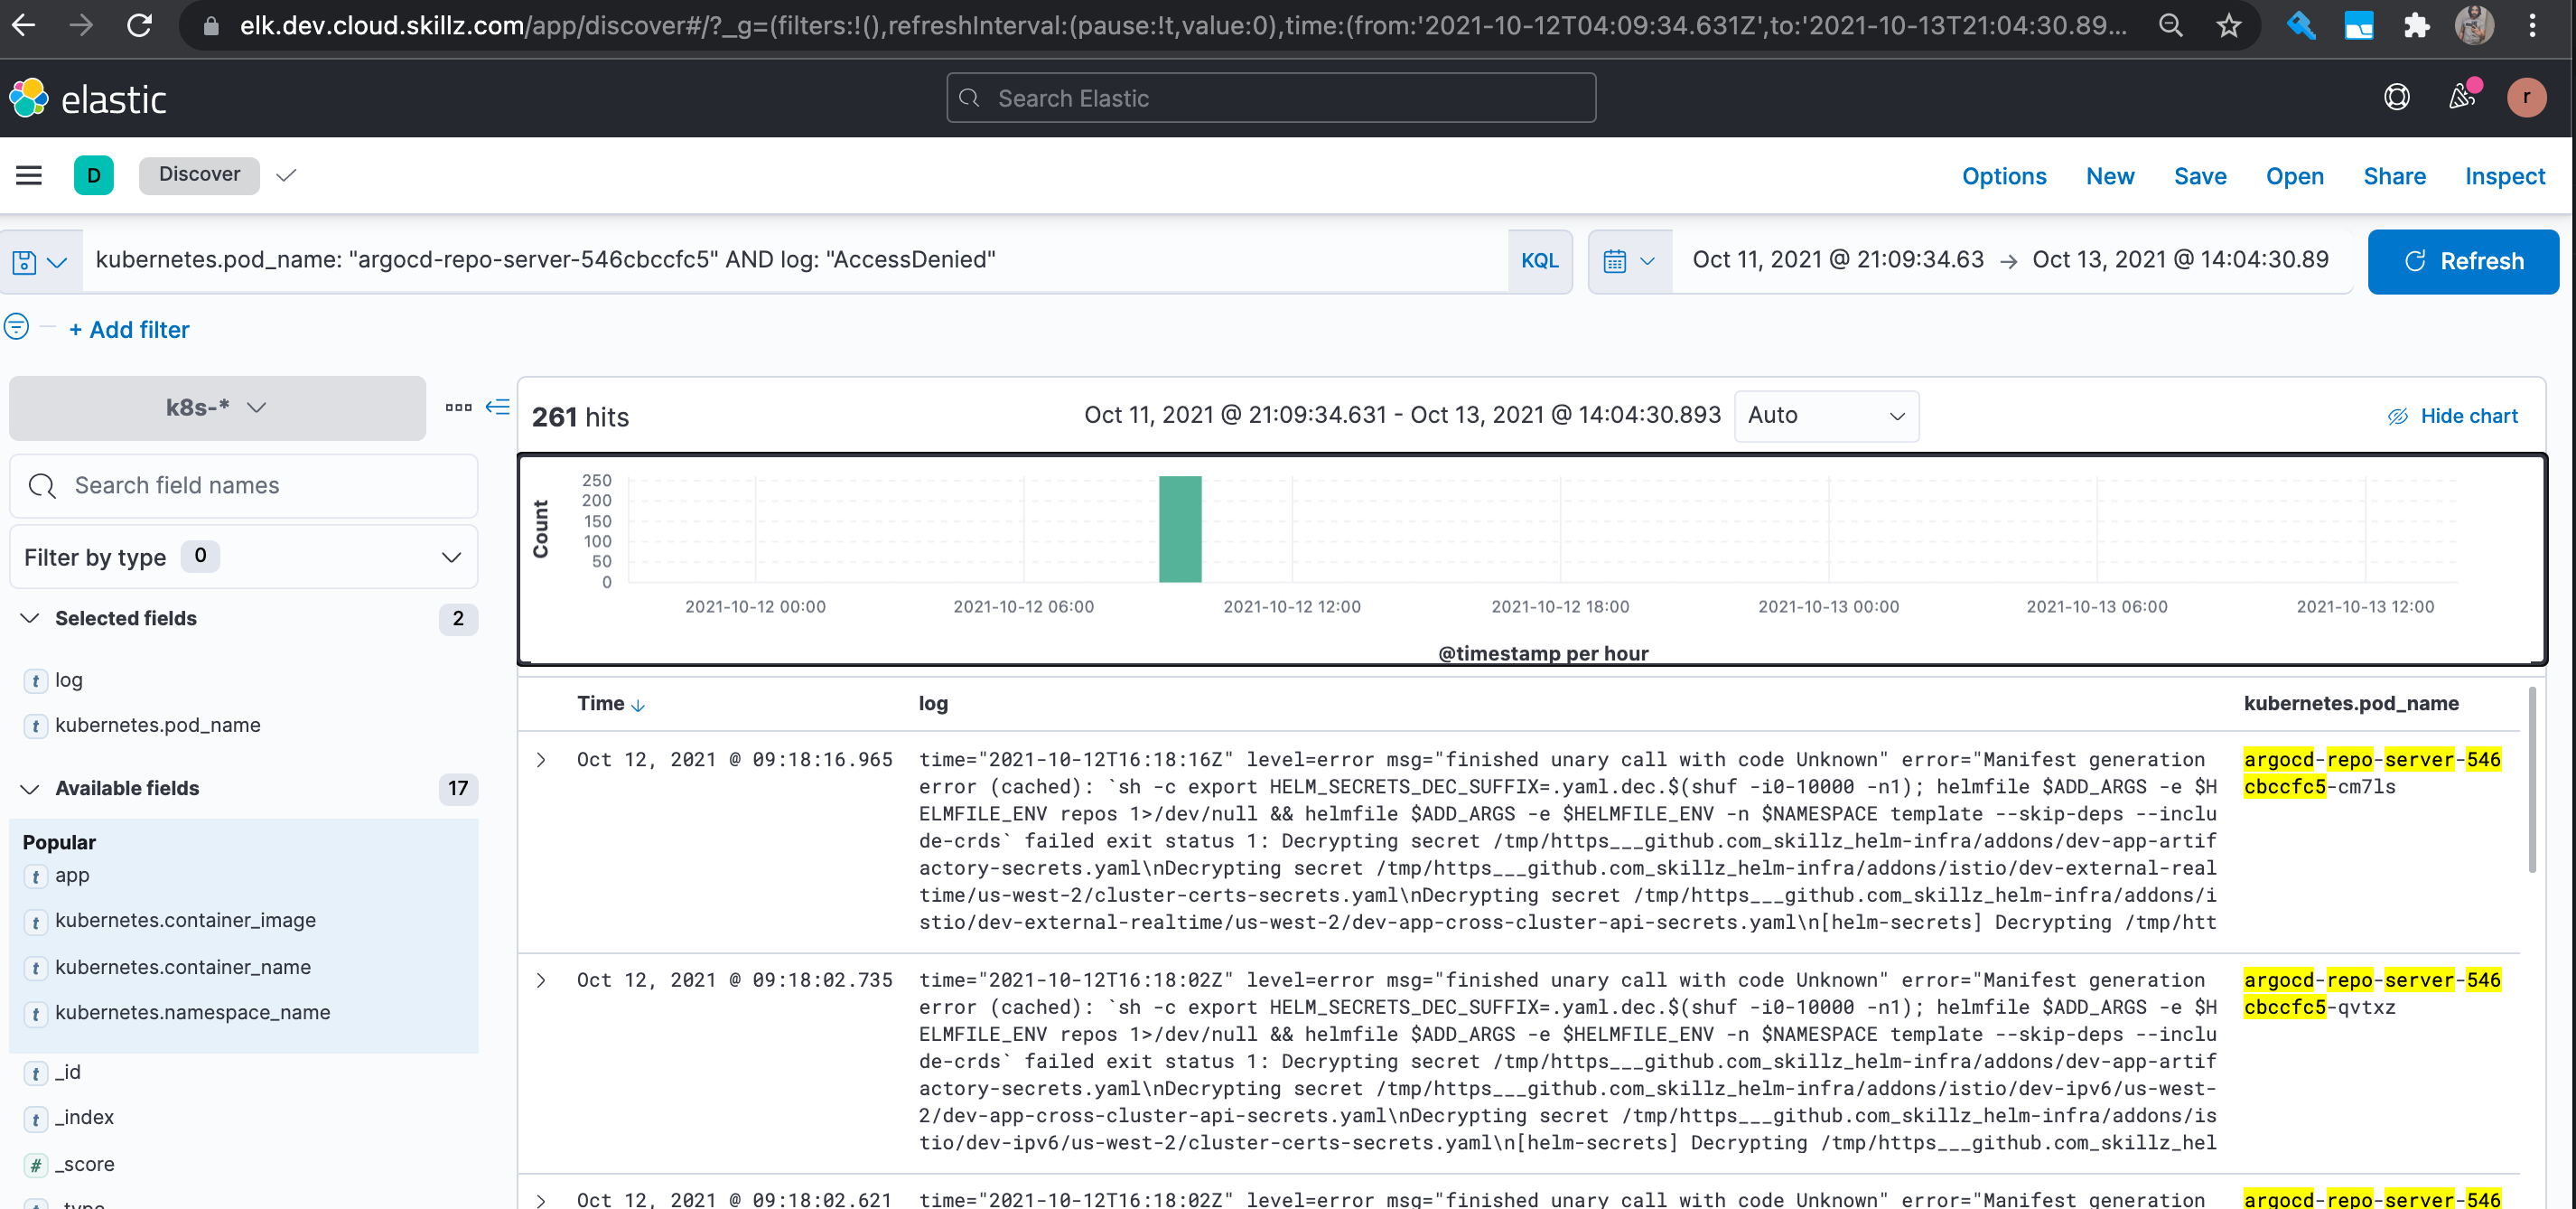
2.1.3fromv2.0.0and also the helm chart to3.24.0from version3.0.02.1.340-50 minutesat the beginning and after some time later the pods can decrypt the secrets just fineAccessDeniederrors stop after sometime for the same set of podsAccessDeniedevents suddenly stop from the same serviceaccountargocd-repo-serverTried the following steps to fix the issue:
helm secrets deccommand but the argocd-repo-server pods were not able to decrypt the secretsChecklist:
argocd version.To Reproduce
Expected behavior
Screenshots
Version
All reactions